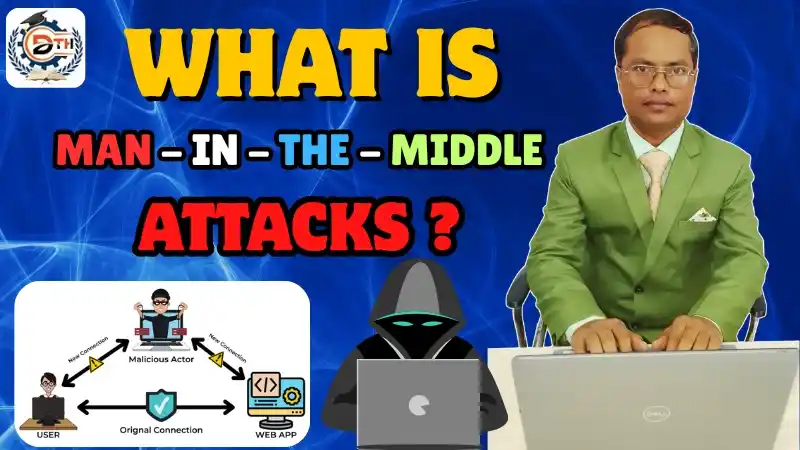
Aaj hum Cyber Security ke ek important aur dangerous attack ke baare mein samjhenge, jise Man-in-the-Middle Attack, ya short mein MITM Attack kaha jata hai.
Simple language mein samjhein to MITM attack mein ek attacker do communicating parties ke beech mein secretly aa jata hai aur unke beech hone wali communication ko read, monitor ya manipulate karne ki koshish karta hai.
Note: Content mein kuch jagah “Man in the Mirror” bola gaya hai, lekin correct cyber-security term Man-in-the-Middle (MITM) hai.
How Can Understand a MITM Attack with a Simple Example?
Maan lijiye A apne friend B ko ek message bhej raha hai.
यदि आप Cyber Security Course सीखना चाहते हैं तो हमारी Technical Team से बात कर सकते हैं!
(HR: 9034756711 | MD: 9017940459)
Normally communication kuch is tarah hogi:
A → B
Lekin MITM attack mein ek attacker beech mein aa jata hai:
A → Attacker → B
A ko lagta hai ki uska data directly B tak ja raha hai, lekin actually attacker communication ko intercept kar raha hota hai.
Attacker:
- Communication ko read kar sakta hai.
- Information ko monitor kar sakta hai.
- Data ko manipulate karne ki koshish kar sakta hai.
- Modified information ko receiver tak bhej sakta hai.
- Sensitive information ko expose kar sakta hai.
Is wajah se MITM attack dangerous ho sakta hai.
What Is the Main Objective of a MITM Attack?
MITM attack mein attacker ka main purpose communication ko intercept karna hota hai.
Complete Lesson in This Video; So Watch Completely!! 👇 👇 👇
Agar communication properly protected nahi hai, to attacker sensitive information tak pahunchne ki koshish kar sakta hai.
For example:
- Username
- Password
- Personal information
- Financial information
- Login details
- Browsing-related information
Agar attacker ko sensitive information mil jaye, to uska misuse kiya ja sakta hai.
MITM Attack Ka Real-Life Example – Public Wi-Fi
MITM attack ko samajhne ke liye public Wi-Fi ek simple example hai. Maan lijiye aap airport, café, restaurant ya mall mein gaye. Wahan aapko ek free Wi-Fi network dikhai deta hai.
Aap sochte hain:
“Free Wi-Fi mil raha hai, connect kar lete hain.”
Lekin problem tab ho sakti hai jab attacker ek fake Wi-Fi hotspot create kar de. Attacker genuine-looking ya similar naam ka Wi-Fi network create kar sakta hai. Aapko network trusted lag sakta hai aur aap usse connect kar sakte hain. Aisi situation mein aapka network traffic attacker ke control mein aa sakta hai aur woh communication ko monitor ya intercept karne ki koshish kar sakta hai.
Public Wi-Fi Use Karte Samay Risk
Public Wi-Fi use karte waqt especially sensitive activities avoid karni chahiye.
Jaise:
- Banking
- Financial transactions
- Important account login
- Sensitive information sharing
- Confidential communication
Agar public network ki authenticity confirm nahi hai, to usse connect karne se bachna better hai.
What is MITM Attack?
MITM attack ko perform karne ke liye attacker different techniques ka use kar sakta hai.
Digital Thinker Help – Best IT Company in Yamunanagar
Kuch common methods hain:
- Fake Wi-Fi Hotspot
- Network Communication Manipulation
- DNS-related Interception
- Session Interception
- HTTPS-related Weaknesses
Ab inhe simple language mein samajhte hain.
1. Fake Wi-Fi Hotspot
Ye MITM attack ka ek common example hai. Attacker ek fake wireless network create kar sakta hai jo kisi genuine network ke naam jaisa lag sakta hai. Maan lijiye aap kisi café ya airport mein hain. Aapko Wi-Fi list mein ek familiar-looking network dikhai deta hai. Aap bina verify kiye connect kar lete hain.
Agar woh attacker ka network hua, to attacker aapke network traffic ko observe ya intercept karne ki koshish kar sakta hai. Isliye unknown Wi-Fi networks ko blindly trust nahi karna chahiye.
2. Network Communication Manipulation
Is technique mein attacker network traffic ko redirect ya manipulate karne ki koshish kar sakta hai.
Normal communication:
A → B
Lekin attacker beech mein traffic ko divert kar sakta hai:
A → Attacker → B
Attacker communication ko read ya modify karne ki koshish kar sakta hai aur phir modified communication ko B tak forward kar sakta hai. Receiver ko directly pata bhi nahi chal sakta ki communication ke beech mein attacker involved tha.
3. Encrypted Communication Ko Target Karna
Aaj ke time mein encryption communication security ka important part hai.
For example, jab aap kisi secure messaging platform par message send karte hain, to message ko encrypted form mein transfer kiya ja sakta hai.
Simple example:
A → Encrypted Data → B
Beech mein attacker data ko capture kar bhi le, to strong encryption ke case mein original information ko samajhna comparatively difficult ho sakta hai.
Isliye strong encryption MITM attacks ke against protection ko improve karne mein important role play karta hai.
What Can an Attacker Steal in MITM Attack?
MITM attack ka impact situation aur communication ki security par depend karta hai. Agar communication properly protected nahi hai, to attacker different types ki information ko target kar sakta hai.
Login Information
Attacker login credentials ko target karne ki koshish kar sakta hai.
For example:
- Username
- Password
- Login session information
Personal Data
Personal information bhi target ban sakti hai.
Financial Information
Financial information attackers ke liye valuable target ho sakti hai.
For example:
- Banking-related information
- Financial account details
- Other sensitive financial data
Browsing Activity
Kuch situations mein browsing-related activity bhi expose ho sakti hai, especially jab communication properly protected na ho.
MITM Attack Ke Common Types
Ab hum MITM attack ke kuch common types ko samajhte hain.
1. Wi-Fi Based MITM Attack
Ismein attacker malicious ya fake wireless network create karta hai.
Public locations jaise:
- Airport
- Café
- Mall
- Restaurant
mein users unknown networks se connect kar sakte hain.
Agar network attacker ka ho, to communication risk mein aa sakti hai.
2. DNS-Related Interception
DNS-related attacks mein attacker user ko incorrect ya fake destination par redirect karne ki koshish kar sakta hai.
Simple example:
A kisi destination B ko data bhejta hai.
Attacker communication ko manipulate karke user ko kisi fake destination C par redirect karne ki koshish kar sakta hai.
User ko lag sakta hai ki woh genuine destination par ja raha hai, jabki traffic kisi attacker-controlled destination ki taraf redirect ho sakta hai.
Is type ke attack mein user ko extra careful rehna chahiye.
3. Session Interception
Session interception mein attacker authenticated session information ko target karne ki koshish kar sakta hai. Online services mein authentication ka purpose ye confirm karna hota hai ki user properly authenticated hai.
Agar attacker session-related information ko compromise kar leta hai, to serious security risk create ho sakta hai. Isliye sessions ko properly secure karna important hai.
4. HTTPS-Related Attacks
HTTPS website communication ko secure karne mein important role play karta hai. Lekin weak configuration ya security warnings ko ignore karna risk ko increase kar sakta hai. Agar browser koi security warning show karta hai, to usse blindly ignore nahi karna chahiye. Security warning ka reason samajhna aur required action lena important hai.
MITM Attack Ke Warning Signs
MITM attack detect karna hamesha easy nahi hota. Lekin kuch warning signs par attention dena chahiye.
1. Unexpected Security Certificate Warning
Agar browser suddenly security certificate warning show karta hai, to usse ignore nahi karna chahiye.
Warning ko read karein aur situation ko properly verify karein.
2. Unknown Wi-Fi Network
Agar aapko koi unknown Wi-Fi network dikhai deta hai, to bina verification ke connect na karein. Especially public places mein network ka naam genuine lagne ke baad bhi verify karna important hai.
3. Repeated Security Messages
Agar website ya browser repeatedly unusual security messages show kar raha hai, to usse seriously lena chahiye. Ho sakta hai system ya connection mein koi security-related issue ho.
4. Unexpected Redirects
Agar aap ek website open karte hain aur repeatedly kisi unexpected website par redirect ho rahe hain, to ye suspicious activity ka sign ho sakta hai. Kisi situation ko ignore nahi karna chahiye.
How Can Stay Safe from a MITM Attack?
Ab sabse important question:
MITM attack se protection kaise milegi
Kuch basic security practices follow karke risk ko reduce kiya ja sakta hai.
1. Unknown Public Wi-Fi Avoid Karein
Unknown public Wi-Fi networks ko unnecessarily use na karein.
Agar network use karna zaroori ho, to pehle verify karein ki woh genuine network hai.
2. Public Wi-Fi Par Banking Avoid Karein
Public Wi-Fi par sensitive banking ya financial activities avoid karni chahiye.
For example:
- Bank account access
- Financial transactions
- Important account login
- Sensitive information sharing
Public network par ye activities karna unnecessary risk create kar sakta hai.
3. HTTPS Check Karein
Website use karte waqt HTTPS aur browser ke security indicators par attention dein. HTTPS secure communication establish karne mein important role play karta hai. Lekin sirf HTTPS dekhkar website ko automatically trustworthy assume nahi karna chahiye. Website ki authenticity bhi verify karni chahiye.
4. Browser Security Warnings Ignore Na Karein
Chrome, Firefox jaise modern browsers security-related warnings show karte hain. Agar browser warning de raha hai, to usse ignore na karein. Pehle warning ko samjhein aur phir appropriate action lein.
5. Operating System Aur Applications Update Rakhein
Apne operating system aur applications ko regularly update karte rahna chahiye. Updates security vulnerabilities ko fix karne mein important role play kar sakte hain.
Isliye:
Regular Updates = Better Security
6. Strong Passwords Use Karein
Har important account ke liye strong aur unique password use karna chahiye. Ek hi password ko multiple accounts par use karne se security risk increase ho sakta hai.
7. Multi-Factor Authentication Enable Karein
MFA – Multi-Factor Authentication account security ko improve kar sakta hai. Maan lijiye attacker ko kisi tarah aapka password pata chal gaya. Agar MFA enabled hai, to login ke liye additional verification required ho sakti hai.
For example:
- Verification code
- Authentication app
- Additional approval
- Other verification methods
Isse attacker ke liye unauthorized access difficult ho sakta hai.
8. VPN Ka Use
VPN ka full form hai:
Virtual Private Network
VPN public network par privacy aur security improve karne mein help kar sakta hai. VPN network traffic ko encrypted tunnel ke through route kar sakta hai, jisse public network par communication ko protect karne mein help mil sakti hai.
Lekin ek important point yaad rakhein:
VPN complete cybersecurity solution nahi hai.
VPN use karne ke baad bhi:
- Phishing se bachna zaroori hai.
- Fake websites se careful rehna zaroori hai.
- Unknown applications install nahi karni chahiye.
- Untrusted platforms se VPN download nahi karna chahiye
Free VPN Se Careful Rahein
Aajkal unknown sources se free VPN applications mil sakti hain.
Kisi bhi random website ya unauthorized platform se software download karna risky ho sakta hai.
VPN ya kisi bhi security application ko preferably official website ya trusted source se hi download karein.
Why is Cyber Security Awareness Important?
Cyber security mein awareness aapki first line of defense ho sakti hai. Agar aapko pata hi nahi hai ki attack kis tarah se hota hai, to usse avoid karna difficult ho sakta hai.
Isliye basic awareness hona important hai.
Sabse pehle samjhein:
- Fake Wi-Fi kya hota hai?
- MITM attack kya hai?
- Security warning ka kya meaning hai?
- Phishing kya hoti hai?
- Strong password kyun zaroori hai?
- MFA kya hai?
- VPN ka role kya hai?
Awareness ke through hum daily life mein unnecessary cyber-security mistakes ko avoid kar sakte hain.
Digital Thinker Help – Cyber Security Training
Agar aap Cyber Security ko professionally learn karna chahte hain, to practical training bhi important hai. Digital Thinker Help Yamunanagar-based company hai jo Cyber Security courses provide karti hai. Course mein theoretical concepts ke saath practical learning par bhi focus kiya jata hai.
Training ke topics mein include kiye gaye areas:
- Cyber Security Fundamentals
- Network Security
- Ethical Hacking Concepts
- Data Protection
- Vulnerability Assessment
- Scanning
- Penetration Testing
- Firewall
- Network Configuration
- Malware Analysis
- Threat Detection
- Live Projects
Yamunanagar ke students ke liye offline learning ke saath online aur weekend learning options bhi available hone ki baat content mein ki gayi hai.
Conclusion – MITM Attack Se Kya Seekha?
Aaj humne Man-in-the-Middle (MITM) Attack ko detail mein samjha.
MITM attack mein attacker communication karne wali do parties ke beech mein aa kar communication ko intercept, read ya manipulate karne ki koshish kar sakta hai.
MITM attacks ke common examples mein fake Wi-Fi networks, DNS-related interception, session interception aur security weaknesses shamil ho sakte hain.
Is attack se bachne ke liye:
- Unknown public Wi-Fi avoid karein.
- Public Wi-Fi par banking activities na karein.
- HTTPS aur security indicators check karein.
- Browser warnings ignore na karein.
- Operating system aur applications updated rakhein.
- Strong passwords use karein.
- MFA enable karein.
- Trusted VPN ka use karein.
- VPN aur applications ko official/trusted sources se download karein.
- Phishing aur fake websites se careful rahein.
Sabse important baat hai ki Cyber Security mein awareness hi hamari first line of defense hai.
Agar hum aware rahenge aur basic security practices follow karenge, to cyber attacks ka risk kaafi had tak reduce kiya ja sakta hai.
Agar aapko ye information useful lagi ho, to video ko like aur share karein, aur channel ko subscribe karein taaki aapko aisi hi informative Cyber Security videos milti rahein.
If this content is valuable for you, then please share it along with your friends, family members, pet lovers or relatives over social media platforms like as Facebook, Instagram, LinkedIn, Twitter, and more.
Do you have any experience, tips, tricks, or query regarding on this? You can drop a comment!